Spatie Roles Permissions by Tharinda Rodrigo
CommunityFilament support for `spatie/laravel-permission`.
 Author:
Tharinda Rodrigo
Package health
Automated checks of this plugin's Composer package
15 checks
- Failed: GitHub Actions pinned to SHA — View details on Plumb
- Skipped: GitLab CI includes pinned to SHA
- Passed: Open security advisories
- Passed: Dependabot PR responsiveness — No open Dependabot PRs.
- Skipped: Renovate MR responsiveness
- Failed: Dependabot or Renovate configured — No dependency updater configuration found. View details on Plumb
- Skipped: Dependency update cooldown configured
- Failed: Provides a security policy — View details on Plumb
- Passed: Abandoned or archived — No consulted source marks the package abandoned (packagist, github).
- Passed: Commit and release recency — Active: last commit 15 days ago; last release 15 days ago.
-
Passed:
composer.lock not committed by library
—
composer.lockis absent from the released dist archive. - Passed: Dist archive is lean
-
Passed:
Current Laravel version supported
—
Package dependencies resolve together with current Laravel
13.0. -
Passed:
Current PHP version supported
—
Constraint
^8.2supports current PHP8.5. - Skipped: Current Symfony version supported
filament/
namespace. Review the source and install at your own risk. Found
malware or an unresolved security issue the author won't
address?
Report it
.
Documentation


This plugin is built on top of Spatie's Permission package.
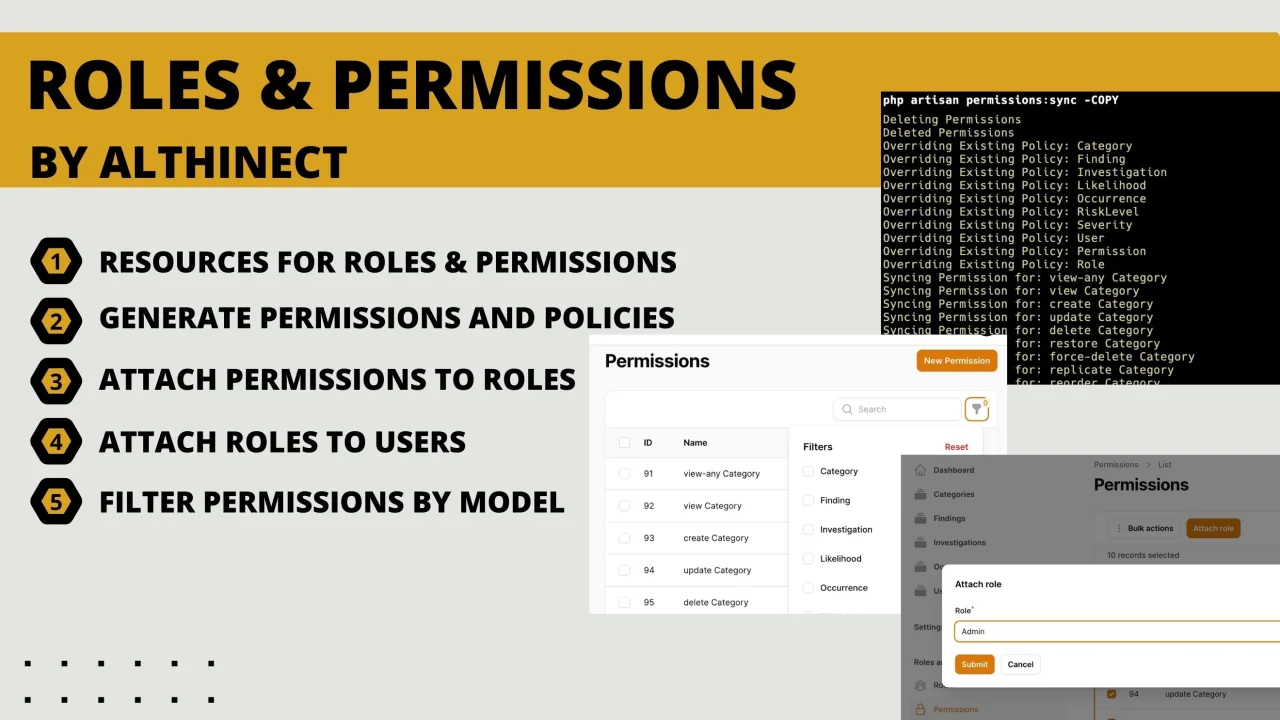
Provides Resources for Roles and Permissions
Permission and Policy generations
- Check the
config/filament-spatie-roles-permissions-config.php
Supports permissions for teams
- Make sure the
teamsattribute in theconfig/permission.phpfile is set totrue
#Updating
After performing a composer update, run
php artisan vendor:publish --tag="filament-spatie-roles-permissions-config" --force
Note that your existing settings will be overriden
#If you like our work Don't forget to STAR the project
#Installation
You can install the package via composer:
composer require althinect/filament-spatie-roles-permissions
Since the package depends on Spatie's Permission package. You have to publish the migrations by running:
php artisan vendor:publish --provider="Spatie\Permission\PermissionServiceProvider"
Add the plugin to the AdminPanelProvider
use Althinect\FilamentSpatieRolesPermissions\FilamentSpatieRolesPermissionsPlugin;

$panel
    ...
    ->plugin(FilamentSpatieRolesPermissionsPlugin::make())
Now you should add any other configurations needed for the Spatie-Permission package.
Note: This will override your existing config file. You can publish the config file of the package with:
php artisan vendor:publish --tag="filament-spatie-roles-permissions-config" --force
You can publish translations with:
php artisan vendor:publish --tag="filament-spatie-roles-permissions-translations"
Don't forget to add the HasRoles trait to your User model.
 // The User model requires this trait
 use HasRoles;
#Usage
#Form
You can add the following to your form method in your UserResource
return $form->schema([
    Select::make('roles')->multiple()->relationship('roles', 'name')
])
In addition to the field added to the UserResource. There will be 2 Resources published under Roles and Permissions. You can use these resources manage roles and permissions.
#Generate Permissions
You can generate Permissions by running
php artisan permissions:sync
This will not delete any existing permissions. However, if you want to delete all existing permissions, run
php artisan permissions:sync -C|--clean
There may be an occassion where you wish to hard reset and truncate your existing permissions. To delete all permissions and reset the primary key, run
php artisan permissions:sync -H|--hard
#Example:
If you have a Post model, it will generate the following permissions
view-any Post
view Post
create Post
update Post
delete Post
restore Post
force-delete Post
replicate Post
reorder Post
#Generating Policies
To generate policies use the command below. This won't replace any existing policies
php artisan permissions:sync -P|--policies
#Overriding existing Policies
This will override existing policy classes
php artisan permissions:sync -O|--oep
#Role and Permission Policies
Create a RolePolicy and PermissionPolicy if you wish to control the visibility of the resources on the navigation menu. Make sure to add them to the AuthServiceProvider.
ℹ️ Info: Laravel 11 removed
AuthServiceProvider, so, in this case, we need to useAppServiceProviderinstead.
use App\Policies\RolePolicy;
use App\Policies\PermissionPolicy;
use Spatie\Permission\Models\Role;
use Spatie\Permission\Models\Permission;

Gate::policy(Role::class, RolePolicy::class);
Gate::policy(Permission::class, PermissionPolicy::class);
#Ignoring prompts
You can ignore any prompts by add the flag -Y or --yes-to-all
Recommended only for new projects as it will replace Policy files
php artisan permissions:sync -COPY
#Adding a Super Admin
- Create a Role with the name
Super Adminand assign the role to a User - Add the following trait to the User Model
use Althinect\FilamentSpatieRolesPermissions\Concerns\HasSuperAdmin;

class User extends Authenticatable{

...
use HasSuperAdmin;
- In the
bootmethod of theAuthServiceProvideradd the following
Gate::before(function (User $user, string $ability) {
    return $user->isSuperAdmin() ? true: null;
});
#Guard Names
When you use any guard other than web you have to add the guard name to the config/auth.php file.
Example: If you use api guard, you should add the following to the guards array
'guards' => [
    ...

    'api' => [
        'driver' => 'token',
        'provider' => 'users',
        'hash' => false,
    ],
],
#Tenancy
- Make sure to set the following on the
config/permission.php
'teams' => true
- Make sure the
team_modelon theconfig/permissionis correctly set. - Create a Role model which extends
Spatie\Permission\Models\Role - Replace the model in the
config/permission.phpwith the newly created models - Add the
teamrelationship in both models
...
public function team(): BelongsTo
{
    return $this->belongsTo(Team::class);
}
- Add the following to the
AdminPanelProviderto support tenancy
use Althinect\FilamentSpatieRolesPermissions\Middleware\SyncSpatiePermissionsWithFilamentTenants;

$panel
    ...
    ->tenantMiddleware([
        SyncSpatiePermissionsWithFilamentTenants::class,
    ], isPersistent: true)
- Use the following within you UserResource
Forms\Components\Select::make('roles')
            ->relationship(name: 'roles', titleAttribute: 'name')
            ->saveRelationshipsUsing(function (Model $record, $state) {
                 $record->roles()->syncWithPivotValues($state, [config('permission.column_names.team_foreign_key') => getPermissionsTeamId()]);
            })
           ->multiple()
           ->preload()
           ->searchable(),
Follow the instructions on Filament Multi-tenancy
#Configurations
In the filament-spatie-roles-permissions.php config file, you can customize the permission generation
If you are using a custom theme from a previous version of filament then there is a possibility that the layout for the roles and permissions will not be full-width. You can set the default column span to 'full' in the config to preserve the v3 default (full-width) layout.
#Security
If you discover any security related issues, please create an issue.
#Credits
#License
The MIT License (MIT). Please see License File for more information.
#Laravel Package Boilerplate
This package was generated using the Laravel Package Boilerplate.
Featured Plugins
A selection of plugins curated by the Filament team
Soft Theme
A theme that gives panels a warm, approachable look with rounded shapes, gentle colors, and serif headings.
 Filament
Compact Theme
A theme that makes data-heavy panels easier to scan by fitting more useful information on each screen.
Filament
Spotlight Pro
Browse your Filament Panel with ease. Filament Spotlight Pro adds a Spotlight like Command Palette to your Filament Panel.
 Dennis Koch